
Software CC answers the question in thirty seconds, and auditors ask the same thing six months later. Ten years ago, spreadsheets and weekly meetings were enough. Today one misconfigured deployment can break a payment system in seconds, so good change control matters more than ever.
Every code change that reaches live production needs reasoning behind its approval. In my experience, clean incident trails turn a stressful night into a short fix.
You will also see a Git-based setup with Git, metrics, tools, standards, and the vocabulary you need. Along the way, you will learn the lifecycle, see where automation helps, learn where judgment matters, and handle every change request.
The Five-Stages
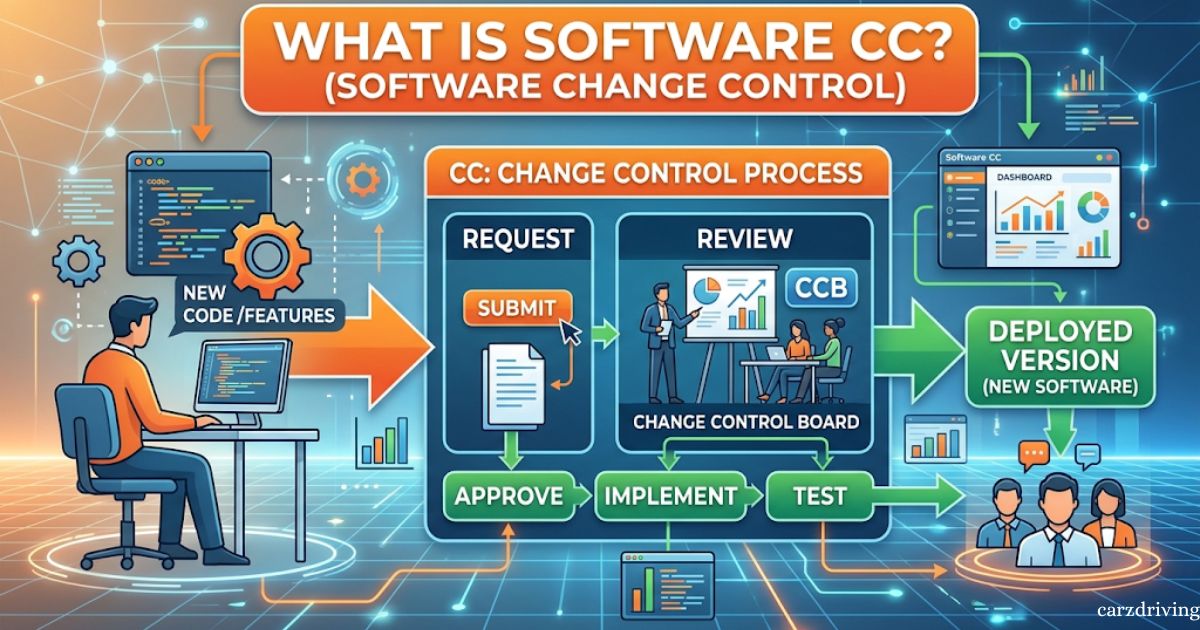
The Request comes first: a developer opens a pull request tied to a ticket and a Git commit, and in a modern setup an infrastructure change proposal works the same way.
Next comes Impact Analysis, which many teams call assessment. Someone checks blast radius, dependencies, risk, data sensitivity, reversibility, and test confidence. A person, an automated scoring rule, or both can do it.
The system records the identity and timestamp, and a sole author never approves alone. Teams save human review for high-risk changes and let routine changes move faster.
Tie it to the exact commit and the artifact you approved. Run a health check after release, and use rollback if it fails.
After release, the post-implementation review checks the outcome. Teams log lessons and close the loop, which makes the next commit safer. Failed changes get a quick human look.
Traditional ITIL Change Control vs. Continuous Delivery Change Management
That model fits legacy systems, monolithic apps, and tightly regulated shops, where manual review and a CAB meeting rule. The paper trail lives in a ticketing system full of manual tickets and tickets and meeting minutes.
Continuous delivery flips this. Automated gates replace most meetings, and selective human review covers the rest. The system builds documentation from Git metadata and pipeline metadata, runs health checks to trigger rollback, and keeps an audit trail of cryptographically linked commit history, deployment logs, linked commits, and approvals.
Most teams land on a hybrid. A payments platform might wave through front-end fixes and send database schema changes to a named approver. That mix keeps automation working where it helps and keeps scale from hurting.
ITIL v4 and its change enablement practice sort work into three types: standard changes, normal changes, and emergency changes. Standard changes stay pre-approved, so a dependency bump with passing tests or a configuration toggle follows a defined procedure with no case-by-case approval.
Normal changes need assessment and authorization, and the depth of review grows with risk. Emergency changes fix a critical vulnerability or an outage. Teams get them reviewed after the fact, but they are never undocumented.
Main Points to Evaluate in Software Change Control Platforms
When you shop for a platform, ignore the marketing page and work through a checklist. Then check risk scoring, immutable audit logs or tamper-evident audit logs, and rollback automation driven by health checks. If a tool misses the first two, walk away.
Look for API-driven webhooks that support ticketing, Slack alerts, chat alerts, and status syncing. Ask for compliance report exports and exportable evidence reports that match frameworks like SOC 2 and ISO 27001.
Several building blocks do the work. For source and review, pick GitHub, GitLab, or Azure DevOps with branch rules and approvals. For change records, use Jira Service Management, ServiceNow, or a simple issue tracker.
For deployment, Argo CD, Flux, Spinnaker, and cloud provider native pipelines all support GitOps. For policy as code, Open Policy Agent and Terraform tooling block bad changes early. For log and evidence storage, append-only storage or object-lock storage keeps records safe from any admin.
A small team rarely needs a heavyweight platform. A pull request template, branch protection, and enforced rules often solve the problem.
Automating Tickets and Status Through Webhooks
Manual ticket updates quietly kill change control processes. Engineers forget, stale tickets pile up, and auditors find gaps. Updating a ticket once a week turns into a chore.
Event-driven updates fix this. A pull request opening creates a linked change ticket through webhooks and an API. A merge event moves the status to in deployment, and a good production deploy closes ticket work and attaches the deployment log. A failed deploy or rollback reopens ticket work and flags for review.
With autopilot on, your ticket system becomes a live mirror of your deployment history. It updates itself, and nobody has to chase it.
Risk Scoring & Decision Matrices
CAB review for every change burns out reviewers, so score each change instead. One older Risk Score Formula multiplies Lines of Code Changed by 0.2. It adds the Target Microservice Criticality Rating (1–5) and subtracts Automated Test Coverage %, using production telemetry. I find mixed units hard to defend, and there is no standard formula, so a developer or auditor will question it.
That formula sets Low Risk Below 15, which CI/CD pipeline gating treats as auto-approved. Medium Risk sits at 15–35 and needs peer approval plus a static code analysis audit log. High Risk sits Above 35 and gets asynchronous CAB review and pre-deployment staging validation.
A three-line bug fix in an internal tool with 95% test coverage earns a score of 4 and ships alone. A 400-line refactor of a payment microservice with 40% test coverage lands above 50 and waits for review. Either way, human attention goes where it matters.
I prefer an additive score built from six factors: blast radius, data sensitivity, change size, reversibility, test confidence, and timing and context. Most factors run 0 to 3, and timing runs 0 to 2. Services that are revenue-critical or safety-critical score high, and so do regulated data and personal data.
A feature flag flip scores low on size, and a manual rollback scores higher than an automated rollback. A strong canary lowers the testing gap, peak traffic adds a point, and a freeze or active incident adds two. The maximum 19 keeps the math simple.
Route by total: 0 to 5 is low, 6 to 10 is medium, and 11 and above is high, where a named approver and a written rollback plan step in. Two override rules help. Anything touching authentication, payments, encryption, access control, or production data schemas stays at least Medium, and a reversibility of 3 forces High.
Here are three worked examples. A fix in an admin tool earns score 1. A payments refactor with thin tests earns score 14. A migration that drops a column in the orders table earns score 11, and the irreversibility override fires too.
Code the rule in Python with a function called risk_tier and a flag named touches sensitive_path. Wire it into a required status check in your pipeline. Keep service inputs in a catalog file, and pull test-coverage and change-size inputs from the build. Then calibrate against your incident history, and let human judgment handle the rest.
Compliance Mapping
Auditors want evidence, because logs prove control. Strong change control shows authorized tested approved documented changes through immutable deployment logs and tamper-evident logs. Check the current text of each standard, since version numbering shifts, and treat the HIPAA link as an interpretation. Auditors rarely demand a CAB meeting, and peer review plus clean logs usually satisfies them.
SOC 2 and SOC 2 Type II point to CC8.1 for change management. They point to CC6.8 for malicious software and unauthorized changes, which protected branches, code review, and scanning support. ISO 27001 uses Annex A 8.32 in the ISO/IEC 27001:2022 2022 edition.
ISO/IEC 27001:2013 used A.12.1.2 under the 2013 numbering, so use the legacy edition only if you still run it. Both want a formal change management procedure with a documented five-stage lifecycle and rollback plans.
NIST SP 800-53 names CM-3, CM-4, and CM-5 for configuration change control, impact analysis, and restricted production access. PCI DSS Requirement 6 covers the cardholder environment and rewards ticket-to-commit linkage. HIPAA 164.312(c)(1) asks for integrity
controls over PHI and electronic health information, so cryptographic audit trails stop silent edits. SOX and ITGC look at financial systems for segregation of duties and approval evidence, and approval gates plus immutable commit-to-deploy logs answer them. Controlled change paths help every framework.
Set up single-click audit reports through a scheduled export. For each change ticket, include the commit SHA, pull request, approver identity, timestamp, risk score, deployment outcome, and rollback events for the audit period. Add test and scan results, emergency changes, and after-the-fact reviews to build an audit evidence pack.
When an auditor asks for Q3 data or a quarter, deliver it in minutes not days. Auditors use sampling from the population, so cover every change.
Common Pitfalls & Anti-Patterns to Avoid
The rubber-stamp CAB is the worst of the anti-patterns. When volume overwhelms reviewers, they approve on autopilot at every CAB meeting. Fix it with tiering and a risk score, and keep a model you calibrate.
Merge is not deploy. Many teams push to the main branch and assume it ships. Tag each release with the commit SHA or artifact, and never deploy from an unrecorded state.
A ghost change is a fix that skips every ticket. It often starts as a hotfix by SSH during incidents, and these untracked hotfixes become an auditor’s worst finding. Restrict direct production access, and make emergency hotfixes open a retroactive ticket, with approval after the fact if needed.
Ticket theater fills tickets with update and fix stuff. Ask for a reason and a rollback note above the low tier. Block approval by the author, self-approval, and a latest push nobody saw. That protects separation of duties with real independent review.
Skip screenshot evidence and export from the system of record. Watch over-tiering: if 80 percent of changes land in High, engineers start gaming inputs, so check the distribution monthly. Plan your emergency path early, because if the right way takes forty minutes and an outage costs a thousand dollars a minute, people route around it.
Software cc
Software cc is no compliance checkbox. It marks the difference between a team that fixes problems in minutes and one that burns an hour on what changed. Build the five-stage lifecycle, automate risk scoring so humans review only the risky work, and tie each deployment to a commit.
Enforce independent review in your Git platform, not in a policy document, and tag the exact artifact. Make emergencies fast but never invisible. Then measure against a baseline, let the numbers show where to tighten or loosen, and grow in stages.
Start small and link commits to tickets this week. That puts you ahead of teams that still run on email threads and spreadsheets. Your compliance reports get easier, MTTR drops, and engineers stop dreading audit season.
FAQs
What is software CC?
Software CC is change control: a structured way to request, assess, approve, and track every code change that reaches production.
Why does software CC matter for audits?
It gives auditors clean evidence, because every commit, approval, and deployment log is linked and tamper-evident.
Do I still need a CAB meeting?
Not for every change: risk scoring and automated gates handle routine work, while only high-risk changes need a named approver.
How does software CC handle emergencies?
Emergency fixes move fast but are never invisible, with a retroactive ticket and an after-the-fact review.
How can a small team start with software change control?
Begin with a pull request template, branch protection, and commit-to-ticket linking, so audit season feels calm instead of stressful.